
Trust Center · Security
Enterprise Security & Data Protection
KitaHQ protects candidate media, transcripts, and organizational recruitment data with multi-layered technical and administrative safeguards. Engineered for data confidentiality, system integrity, and continuous availability, our security framework allows hiring teams to operate with total confidence.
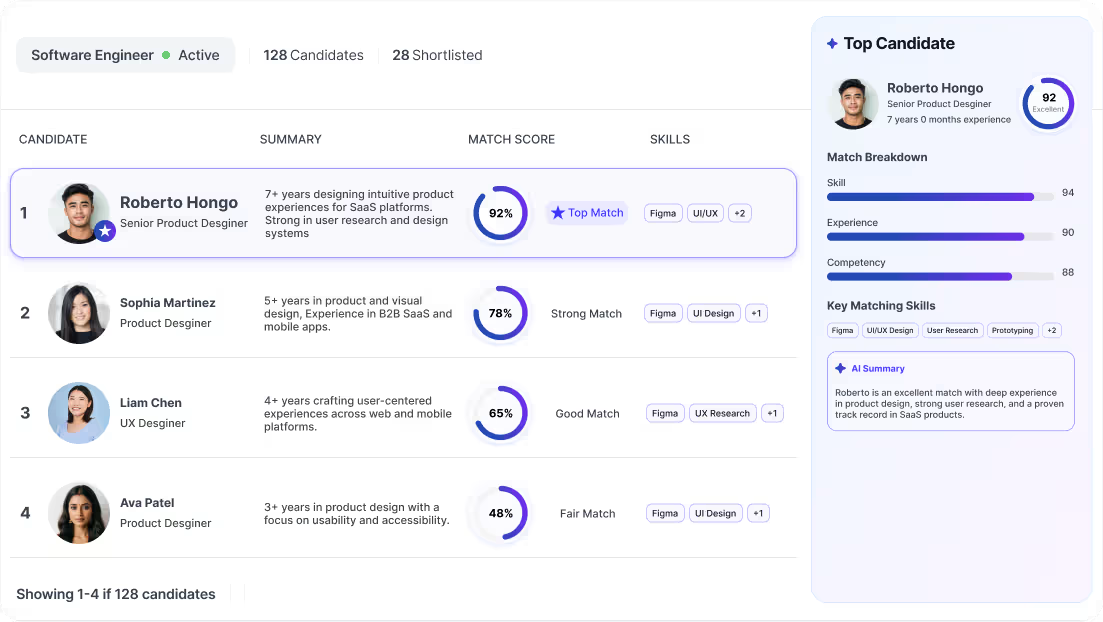
Hiring context
CVs · interview responses · transcripts · recordings · reports
Core Security Controls
These controls support transparency, consistent criteria and human accountability. Their effectiveness also depends on employer configuration, criteria, safeguards and human use.

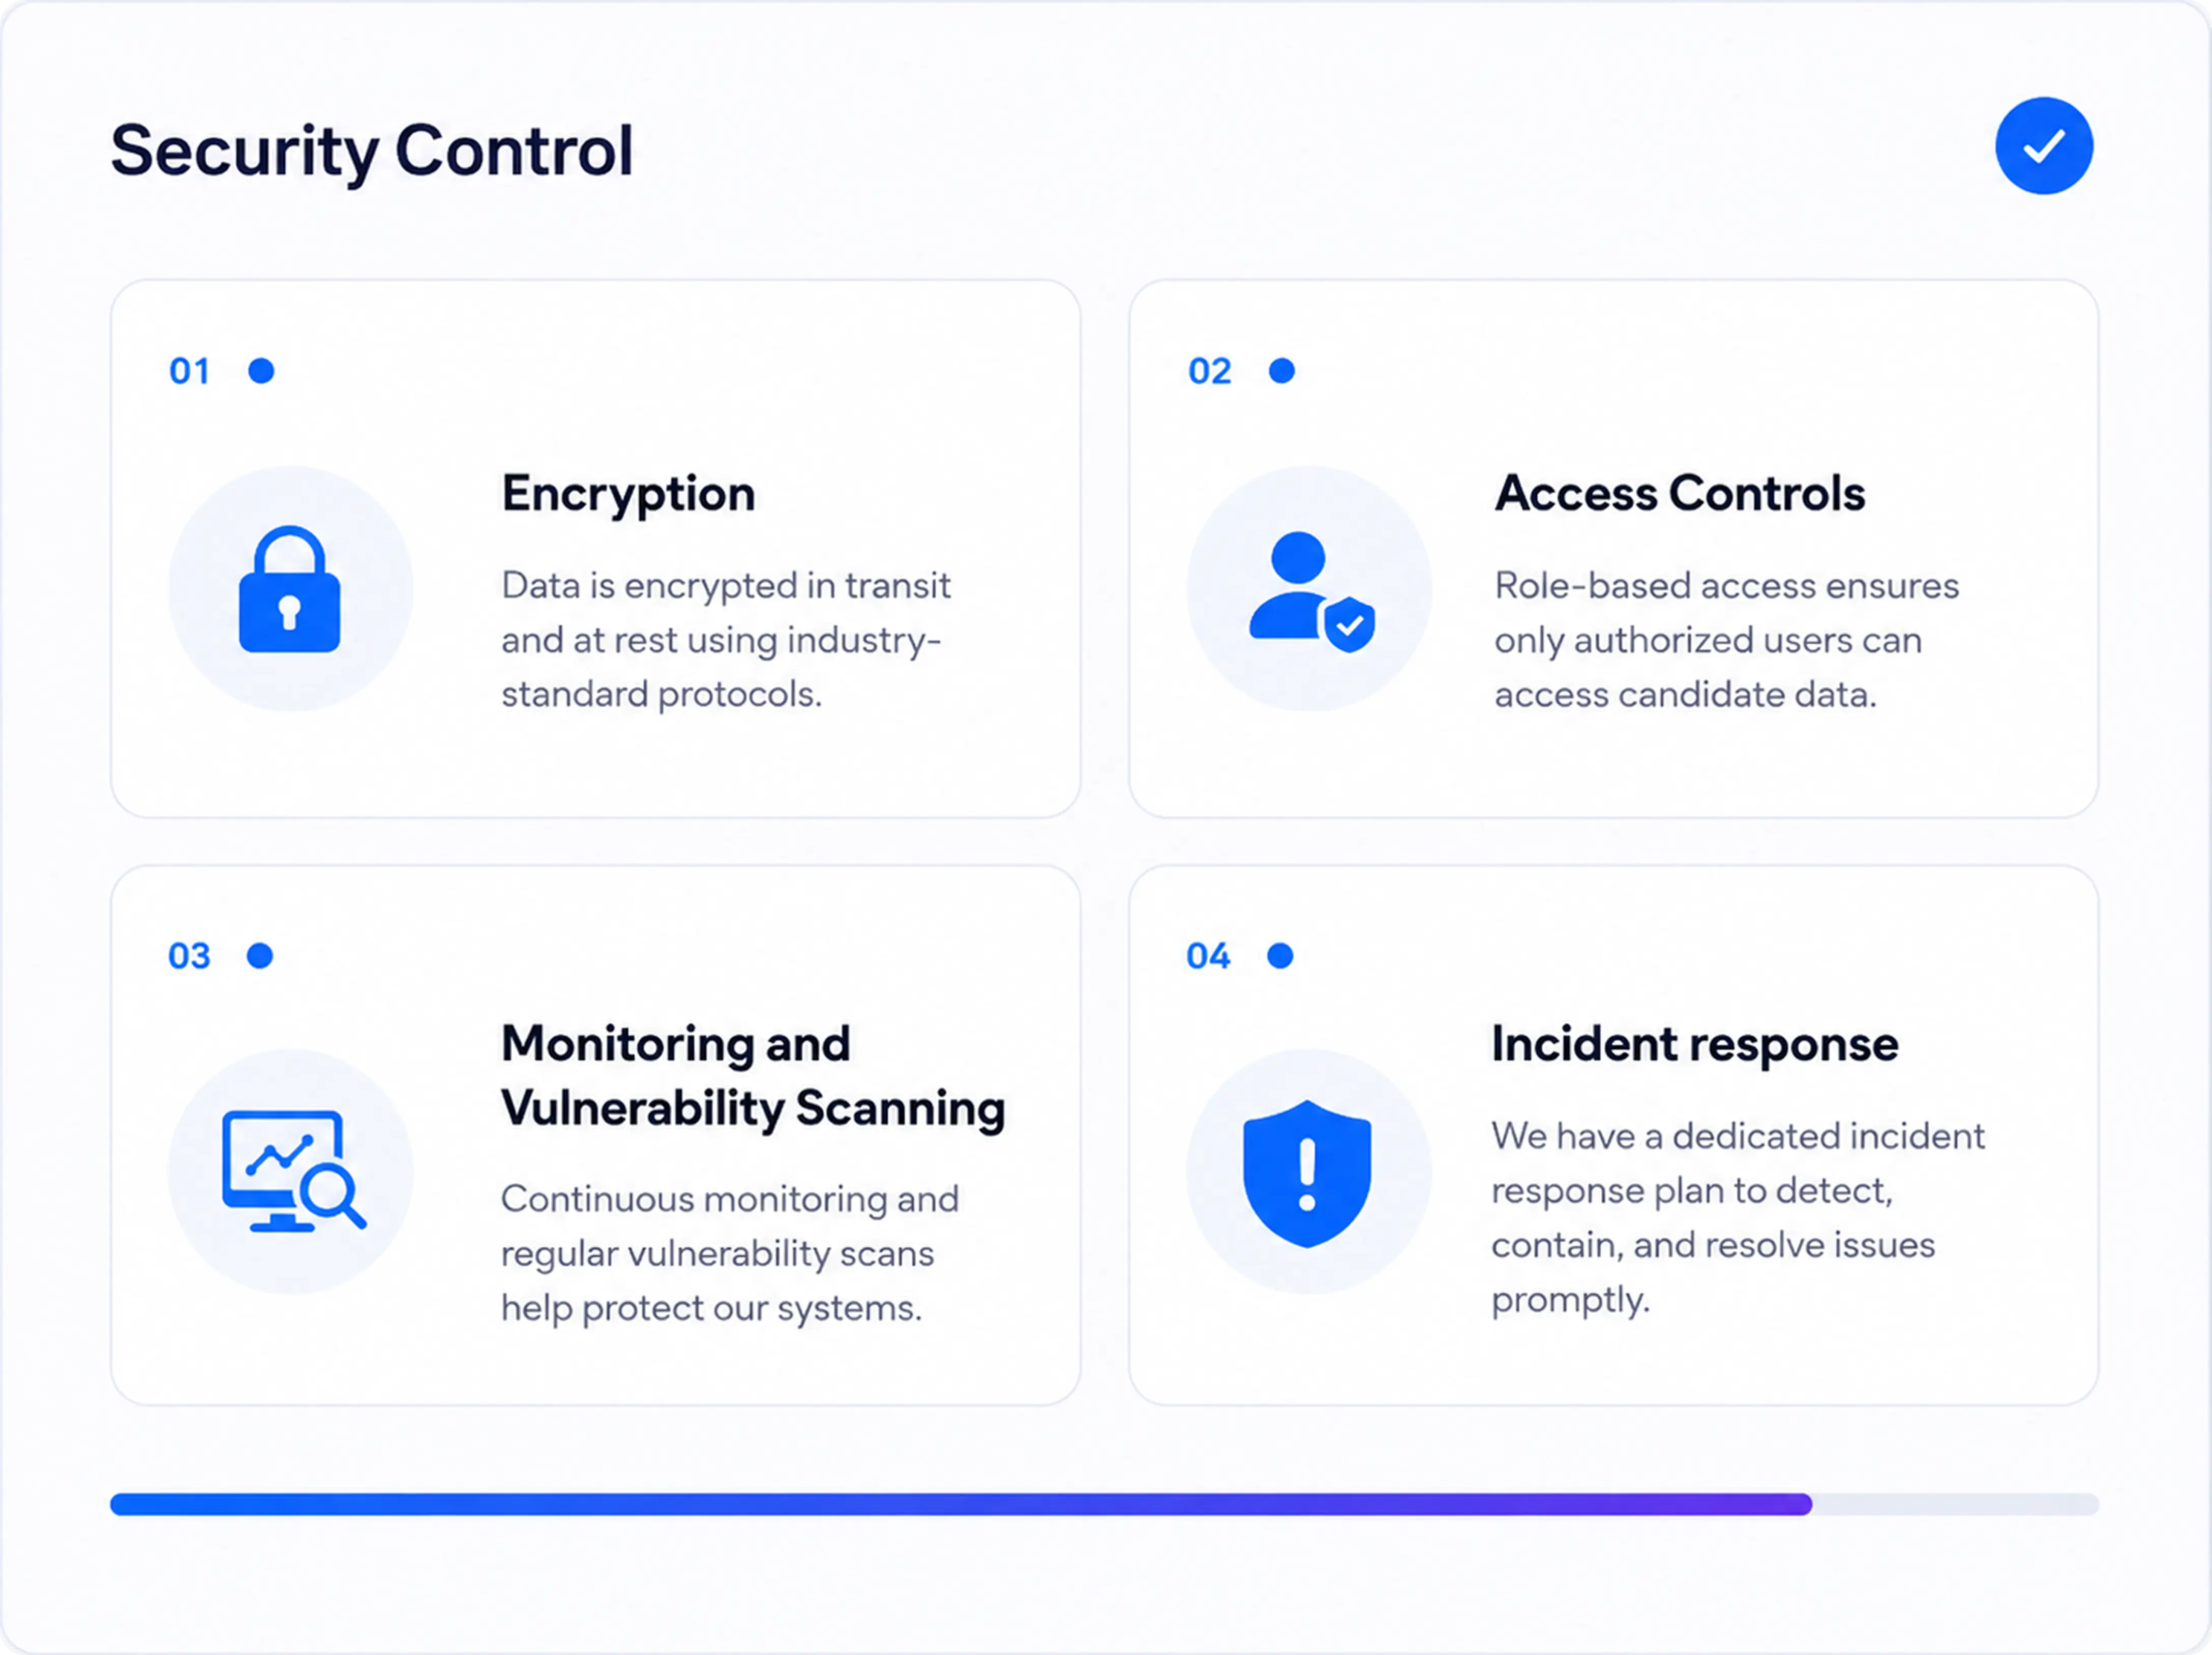
Encryption

Data is encrypted in transit and at rest.
Access Controls
Role-Based Access Control (RBAC) and Multi-Factor Authentication (MFA) enforce strict principle-of-least-privilege access.
Monitoring and Scanning
Continuous infrastructure monitoring, automated code scanning, and regular vulnerability assessments identify and remediate potential security risks.
Incident Response
Documented incident response procedures guide our team to detect, contain, investigate, and notify customers in accordance with contractual and regulatory breach requirements.

EVIDENCE
CONTROL REFERENCE
Compliance Mapping & Evidence
SOC 2 Alignment: KitaHQ internally maps its technical and operational controls to selected criteria within the AICPA Trust Services Criteria (SOC 2) for security and confidentiality.
CONTROL
EVIDENCE
REVIEW
Data Lifecycle

Zero AI Model Training
Candidate resumes, video responses, audio, and interview transcripts are never used to train KitaHQ or third-party AI models.
Employer-Driven Data Retention
Recruitment data is retained according to your organization's specific policy configuration, customer agreements, and statutory requirements.
Trusted Infrastructure & Processing
KitaHQ utilizes enterprise-grade cloud hosting and AI infrastructure. Cross-border data transfers comply with international data protection laws, protected by strict contractual safeguards, encryption, and our Privacy Notice.
Automated Deletion Controls
Employers maintain full ownership over data retention timelines and can execute automated deletion workflows across all candidate records and underlying processing systems upon request.
The Shared Responsibility Partnership
Security is a joint commitment between KitaHQ and your administration team:
KitaHQ Operations
Securing cloud infrastructure, protecting data at rest/transit, maintaining platform availability, and applying vulnerability patches.
Employer Workspace Controls
Provisioning and revoking recruiter credentials, enforcing internal password and MFA policies, configuring review access, and safeguarding interview invitation links.
Candidate & User Best Practices
Users and candidates must safeguard login credentials, avoid sharing interview access links, and refrain from sending passwords over email.
Vulnerability & Support Channels
Security & Vulnerability Reporting
Report potential security concerns or system vulnerabilities directly to support@kitahq.com.

Technical Support
Reach out to support@kitahq.com for system assistance or platform bugs.
Privacy & Data Rights
Send privacy-related inquiries and data subject requests to privacy@kitahq.com.
AI System Safeguards & Data Isolation
KitaHQ’s public security assurance is supported by the following documented controls:
01
Zero Model Training
Candidate resumes, video responses, and interview transcripts are never used to train public or proprietary AI models.
02
Tenant Data Segregation
Customer workspace data is logically separated to eliminate any possibility of cross-organization data access or leakage.
03
Data Retention & Erasure
Data is retained strictly in accordance with customer instruction and applicable privacy laws, supporting automated deletion workflows upon request.
PRIVATE
PROTECTED
ISOLATED
Country-Specific Security & Compliance Frameworks

United States

Controls align with FTC data security guidelines, state-level breach notification mandates, and CCPA/CPRA standards through enforced encryption, role-based access controls, and documented incident response procedures.

United Kingdom
Built to meet UK GDPR and Data Protection Act 2018 expectations, ensuring appropriate technical and organizational measures (TOMs) protect candidate records across all processing steps.

Canada
Supports PIPEDA and provincial privacy standards through strict data isolation, encrypted transit/storage, and auditable access governance.

Australia
Supports Australian Privacy Principle 11 (APP 11) under the Privacy Act 1988 by enforcing controls designed to prevent unauthorized access, data misuse, or loss.

New Zealand
Aligns with Information Privacy Principle 5 (IPP 5) under the Privacy Act 2020 through resilient cloud infrastructure safeguards and strict user access controls.

Singapore
Fulfills PDPA Protection Obligation expectations by applying enterprise-grade encryption and multi-factor authentication to candidate data environments.

Malaysia
Meets Personal Data Protection Act (PDPA 2010) Security Standards by enforcing administrative and technical access boundaries across all employer workspaces.

Indonesia
Aligns with Law No. 27/2022 (UU PDP) technical data protection requirements, guaranteeing candidate media encryption and strict local access governance.

Germany and the European Union
Meets Article 32 GDPR and BDSG requirements for technical and organizational safeguards through AES-256 encryption at rest, TLS 1.2+ in transit, and continuous vulnerability monitoring.
Explore KitaHQ Trust

Responsible AI
Learn what KitaHQ's AI processes, what outputs it creates, how those outputs should be interpreted, where automation may occur and how human responsibility is maintained.


Fair Hiring Practices
See how job-related criteria, structured interviews, recruiter reviews, accommodations and employer responsibilities fit together.

Candidate Guide
Understand how to prepare for a KitaHQ AI video interview, how AI is used, how to request help and where hiring decisions are made.